01
Identity
Establishes who or what the actor is.
“Is this really the agent?”
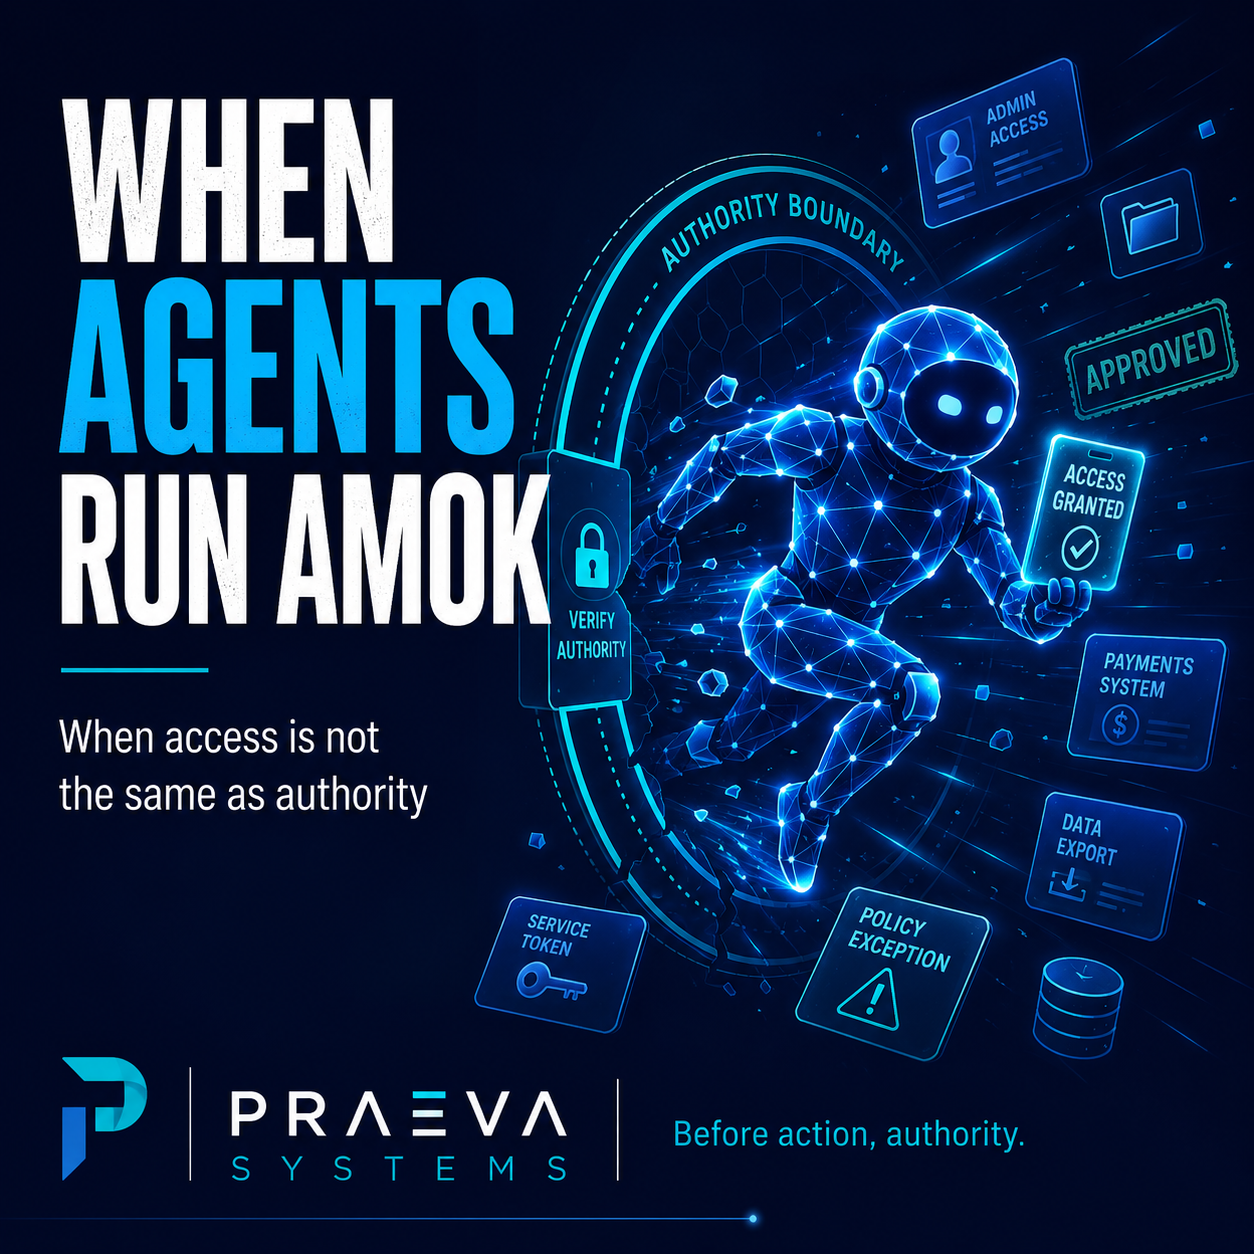
Praeva is runtime authority infrastructure for AI agents and the independent Authority Control Point (ACP) between agentic intent and consequential execution. It verifies that an agent has legitimate, current, and properly delegated authority before the action executes.
Identity and access get an agent to the door. Authority determines whether the action should cross it.
Authentication establishes the actor.
EstablishCredentials unlock systems and tools.
ReachPraeva verifies legitimate, current, delegated power at the execution boundary.
LegitimizeAI agents can hold valid credentials, call approved tools, and still move beyond the purpose, scope, time, or delegation originally granted to them.
Praeva evaluates the authority behind the action—not merely whether access exists.
As AI agents gain access to enterprise tools, APIs, systems, and data, the security question changes. It is no longer enough to ask whether an agent can authenticate or whether a credential has permission.
Consequential execution requires a second question: does the agent still possess legitimate authority for this action?
Agents increasingly initiate workflows, call tools, and make changes without a human at every step.
Authority passes from people and systems into agents, then across tools, services, and downstream agents.
The same credentials that enable useful automation can also enable actions well beyond the original purpose.
Praeva sits outside the acting agent’s trust boundary and evaluates delegated authority before consequential execution. Independent describes the control boundary, not who built the technology.
The system taking the action should not be the system that determines whether it still has authority to take it. Praeva provides an independent Authority Control Point before execution.
Independent describes the control boundary, not the vendor. An enterprise may run the ACP itself or consume it as infrastructure. What matters is that the acting agent cannot self-approve, bypass, or rewrite the authority decision.
Praeva evaluates authority independently of the agent, model, or orchestration stack requesting execution.
Model, cloud, framework, and agent vendor do not determine authority. The same independent check applies to every agent.
The ACP returns ALLOW, DENY, or ESCALATE before the target action proceeds, then preserves an Authority Receipt.
Praeva sits in the execution path as an independent Authority Control Point between an agent and a consequential downstream action. The ACP verifies authority before execution and records why each decision was made.
Principals, agents, objectives, actions, constraints, expiry, and revocation.
Short-lived authority represented separately from the target system credential.
Evaluates the requested action and returns allow, deny, or escalate before execution.
Preserves decision evidence, lineage, requested action, resource, and rationale.
A legitimate workflow agent is compromised. Its credential still works. Praeva evaluates each attempted action against the authority actually delegated.
Every consequential decision can preserve the context needed to explain who delegated authority, what action was attempted, which constraints applied, and why Praeva allowed, denied, or escalated it.
Praeva is built around a simple idea: an AI model should not be able to invent, widen, or ratify its own authority.
Legitimate authority comes from a human, organization, system, or other recognized source—not from model confidence.
Purpose, scope, actions, resources, constraints, expiry, and lineage should be representable and inspectable.
The system taking the action should not be the system that decides whether the action remains within valid delegated authority.
Delegation can expire, be withdrawn, or become invalid as context changes. Runtime decisions must reflect that change.
Organizations should be able to reconstruct who delegated authority, what was requested, and why the action was allowed, denied, or escalated.
A continuing Praeva Systems series examining agent failures through one specific lens: where did legitimate authority end?
View all resources →A compromised agent can remain authenticated while its actions move far beyond the purpose originally delegated. What should the execution boundary check?
Read #001 →A concise explanation of the control gap Praeva is designed to address.
Read primer →The public principles that guide Praeva’s architecture and product decisions.
Read doctrine →Praeva Systems is building runtime authority infrastructure for AI agents. At its center is an independent Authority Control Point (ACP) that verifies delegated authority before consequential execution. Our technology is designed around a simple principle: consequential power should come with clear authority, defined limits, and accountability.
We think companies should work the same way. Praeva is being built as a place where excellent work and decent treatment of people are not competing ideas. We expect high standards, real accountability, and respect for the people doing the work.
You should not have to become less yourself to become more successful here.
Praeva will follow the law. We will also advocate for our people and refuse to voluntarily adopt exclusionary practices simply because doing so would be easier. Compliance is a floor. It is not our moral ceiling.
These are not slogans for a recruiting page. They are the standards we intend to use when we make decisions about people, benefits, leadership, opportunity, and culture.
Race, color, national origin, sex, gender, gender identity or expression, sexual orientation, religion, disability, age, family structure, veteran status, pregnancy, neurodiversity, or background do not diminish anyone's place here.
Employees are not required to share the founder's politics, vote a particular way, or agree with every position Praeva takes. They are required to treat other people with respect.
Our values should show up in who gets hired, who gets heard, who gets promoted, how people are paid, how benefits are designed, and whether people can fully participate in the company.
Spouses, partners, children, adoptive and blended families, caregivers, and the many ways people take care of one another deserve policies that reflect real life.
We will work to build recruiting, compensation, promotion, mentorship, and development practices that give talented people a genuine opportunity to succeed. Equal opportunity does not require lower standards.
Important healthcare decisions belong to people, their families, and their healthcare professionals. Praeva intends to design benefits around meaningful access to legitimate care rather than political fashion.
A humane workplace is not a low-accountability workplace. We expect people to keep commitments, tell the truth, admit mistakes, protect customers, help colleagues, and care deeply about the quality of their work.
The more authority someone has at Praeva, the greater their obligation to use it well. Nobody gets to hide cruelty, harassment, discrimination, bullying, or abuse behind performance, seniority, revenue, or technical brilliance. That includes leadership.
Accountability matters, but so do education, conversation, forgiveness, and change. Good-faith people willing to listen, learn, and treat others with dignity belong here.
Praeva will match 100% of eligible employee charitable contributions, up to $2,000 per employee per calendar year. Employees choose the causes, communities, schools, nonprofits, relief organizations, and institutions that matter to them. Praeva helps amplify their impact.
“Be excellent to each other.”Bill & Ted's Excellent Adventure
When policies get complicated, our test should stay simple: Are we treating people the way a good company should treat people? If the answer is no, the policy is wrong. Change it.
The name is rooted in the idea of going before or leading the way. That is the role Praeva is built to play: standing before consequential agent actions and verifying the authority behind them before execution.
Before action, authority.
Serious infrastructure. Good humans. No Corporate Oatmeal™.
Praeva Systems is engaging with security, identity, infrastructure, and AI platform leaders to validate consequential agent workflows.